Building Trusted Access For Next-Gen Data Centres Critical To Australia’s National Infrastructure.
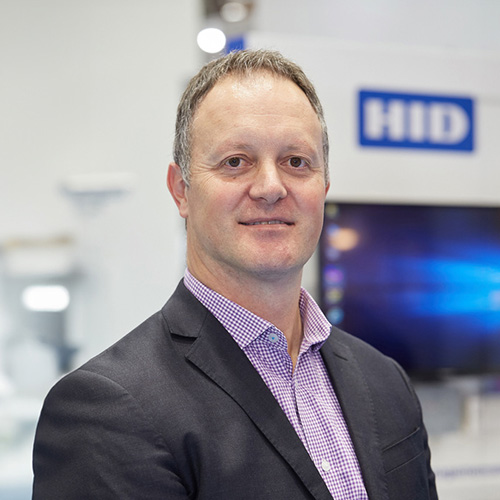
Building Trusted Access For Next-Gen Data Centres – Australia’s data centre market is entering a new phase with the rapid adoption of cloud computing and AI driving unprecedented demand for digital infrastructure, with developers planning facilities at a scale that would have seemed extraordinary only a few years ago, writes HID’s Steve Katanas.
The runaway expansion reflects more than the growth of an individual industry. Data centres are rapidly becoming critical national infrastructure, providing the physical foundation for Australia’s businesses, government services, communications and, increasingly, its AI capabilities.
Much of the conversation around new facilities understandably focuses on power, cooling, connectivity, resilience and sustainability. Yet there is another fundamental question that deserves equal attention: how will people move securely through these facilities, today and for decades to come?
For developers and operators, physical access control is no longer simply about securing doors. It is about establishing trusted identity throughout a facility and ensuring the right people can access the right areas at the right time.
Data centres are designed to operate for decades, but security requirements, authentication technologies and operational needs will continue to evolve. Access control infrastructure must be able to support that evolution.
Layered Security The Starting Point
Layered security has long been fundamental to data centre design. Access privileges become increasingly restrictive as people move from the perimeter through building entrances and into data halls and other sensitive areas. Authentication requirements can strengthen at each layer according to an individual’s role, the sensitivity of the environment and the level of risk.
But layered access itself is no longer a differentiator. Any credible security architecture should be capable of implementing it.
The more important question is what sits underneath that layered model – effective physical security starts with confidence in identity. Employees, contractors, service providers and visitors all need to be authenticated securely and consistently, while operators need the flexibility to apply different levels of access according to role and circumstance.
This becomes particularly important as digital and physical security increasingly converge.
Don’t Build Yourself Into A Corner
A data centre’s access control system may appear to be a relatively small decision during the design and construction phase. Its consequences, however, can last for decades.
A closed, single-vendor architecture may perform perfectly well on day 1, but over time it can constrain an operator’s choices. New authentication technologies may require wholesale replacement. Expansion may mean purchasing more proprietary hardware, while integration with other systems can become unnecessarily complex.
The system that initially looked like a safe choice can ultimately become a barrier to adapting as security requirements change.
For infrastructure intended to support Australia’s long-term digital and data sovereignty ambitions, that is a significant but avoidable risk. This is why open architecture matters.
Open, interoperable platforms allow operators to integrate access control with a wider range of technologies, including video surveillance, identity management and operational systems. They also make it easier to introduce new authentication technologies as requirements evolve.
The principle is straightforward: operators should be able to select the technologies that best meet their requirements today while retaining the flexibility to adopt new solutions as those requirements change.
The scale of Australia’s data centre growth makes these decisions increasingly consequential. Physical access control may not be the most visible element of a data centre build, but it is one of the foundations that will remain in place long after construction is complete.
The question for operators is therefore bigger than which reader or credential to specify.
They should ask whether the access control architecture is built around trusted identity, whether it supports open standards and interoperability, whether it can accommodate future authentication technologies, and whether the provider and partner ecosystem will be there to support the facility throughout its operational life.
Get that foundation right, and Australia’s data centres will have the freedom to adapt as the technology around them changes. Get it wrong, and every future decision becomes harder.
You can learn more about HID here or read more SEN news here.
“Building Trusted Access For Next-Gen Data Centres Critical To Australia’s National Infrastructure.”