-

- Advertisment -
  • HID TREND REPORT
  • AcuSeek
  • ASSA ABLOY Aperio IL100 – design-driven wireless access reader. Register your interest.

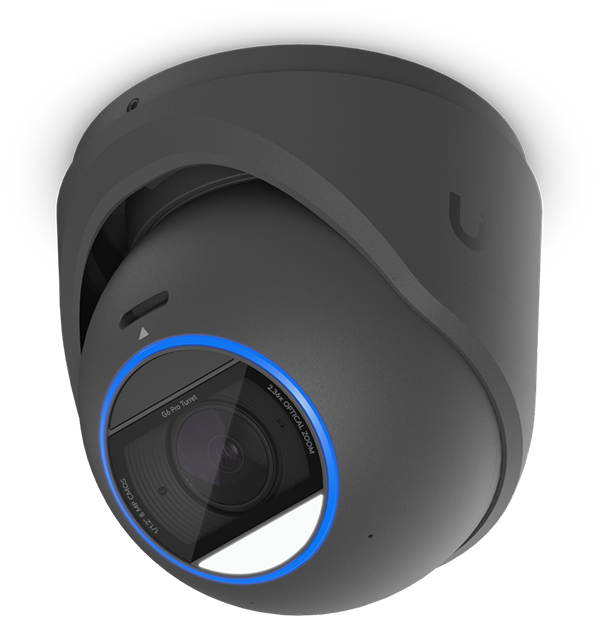
Ubiquiti Patches 3 Maximum Severity UniFi Flaws

Ubiquiti Patches 3 Maximum Severity UniFi Flaws In Protect, UniFi OS And Talk, With Around 3200 Australian Consoles Exposed.

Ubiquiti Patches 3 Maximum Severity UniFi Flaws – Ubiquiti’s Security Advisory Bulletin 067, released on August 26, fixes 22 critical vulnerabilities across the UniFi range. 3 of them are rated CVSS 10.0, in UniFi Protect, UniFi OS Server and UniFi Talk, and all 3 can be exploited without authentication or any user interaction.

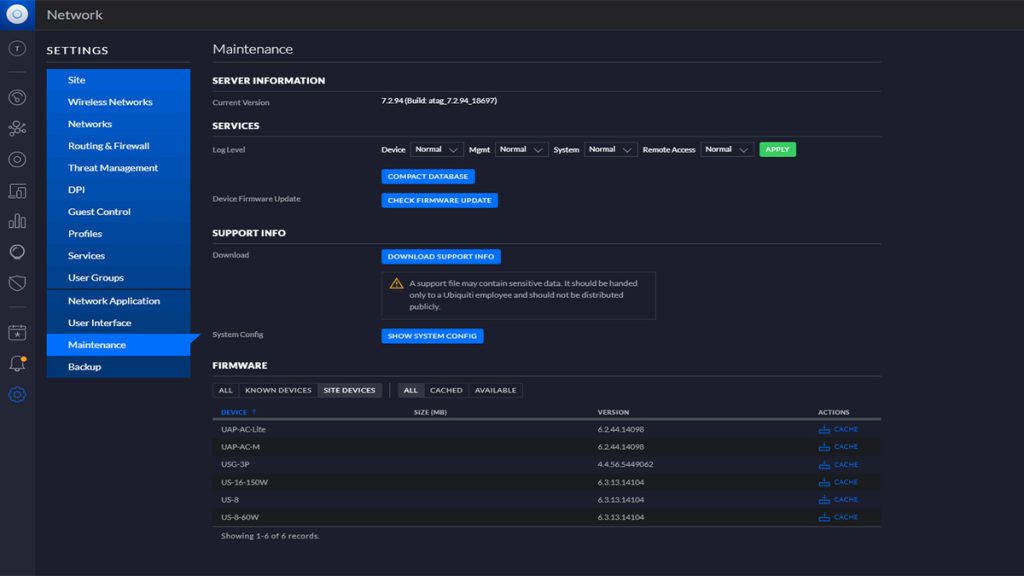
If you install or maintain UniFi Protect video or UniFi Access doors, this one matters. Internet scanning firm Censys counted around 3200 Australian UniFi OS management interfaces exposed to the internet the day after disclosure – and the last time Ubiquiti published a bulletin like this, attackers didn’t take long to act on it.

UBIQUITI has become a serious force in the SMB security market over the past few years. Protect cameras and NVRs, Access readers and hubs, and Talk VoIP now run on the same consoles as the network itself. That convergence is a big part of the appeal for installers and end users alike. It also means that when the platform has a bad day, cameras, doors and phones have a bad day together.

Security advisory · Ubiquiti SAB-067 · 26 August
Action required
3× CVSS 10.0Maximum-severity flaws
3,200AUExposed consoles (Censys)
All three top-rated flaws — in Protect, UniFi OS Server and Talk — are exploitable remotely with no credentials and no user interaction, as stated in Ubiquiti’s bulletin.
Days since disclosure of a 33-day precedent
Counting from the 26 August disclosure.
22Critical CVEs fixed
6Product lines patched
100K+Consoles exposed worldwide
0Credentials needed to exploit
Flaw counts, severity ratings and the 26 August date as published by Ubiquiti (SAB-067). Exposure counts as scanned by Censys on 27 August. The day counter and the 33-day reference — the patch-to-botnet interval Ubiquiti’s earlier SAB-064 flaws ran — are SEN calculations, computed live.

The 3 maximum severity flaws are:

Ubiquiti Patches 3 Maximum Severity UniFi Flaws
  • a command injection vulnerability in UniFi Protect (CVE-2026-77537)
  • a CRLF injection in UniFi OS Server that leads to authentication bypass (CVE-2026-77550)
  • a vulnerability in UniFi Talk (CVE-2026-77554)

All 3 sit at the top of the CVSS scale, and all 3 can be exploited remotely by an attacker with no credentials and no help from a user.

Importantly for access control installers, UniFi Access is in the bulletin as well. It has 4 vulnerabilities (CVE-2026-77543, CVE-2026-77546, CVE-2026-77547 and CVE-2026-77553), all fixed in Access 4.3.5. Protect AI Key and UniFi Network also receive fixes.

The fixed versions are:

  • UniFi Protect 7.2.105 or later
  • UniFi OS Server 5.1.37 or later
  • UniFi Talk 5.3.2 or later
  • UniFi Access 4.3.5
  • Protect AI Key 2.2.6
  • UniFi Network 10.5.67
Fixed versions · SAB-067
Is every console you touch on these builds?
Tap the products you look after to build a verify list — or read all six below. Anything behind these versions carries the SAB-067 flaws.
UniFi ProtectCVE-2026-77537 · CVSS 10.0 · command injection≥ 7.2.105
UniFi OS ServerCVE-2026-77550 · CVSS 10.0 · auth bypass≥ 5.1.37
UniFi TalkCVE-2026-77554 · CVSS 10.0≥ 5.3.2
UniFi Access4 CVEs · 77543 / 77546 / 77547 / 77553≥ 4.3.5
Protect AI KeyFixes included in SAB-067≥ 2.2.6
UniFi NetworkFixes included in SAB-067≥ 10.5.67
Fixed versions as published by Ubiquiti in SAB-067; “or later” applies per the bulletin. Ubiquiti’s advice, echoed by SEN: don’t assume auto-update has done the job — log in and look.

How Exposed Is Australia?

Censys scanned for affected systems on August 27, the day after disclosure. It found more than 100,000 UniFi OS management interfaces exposed to the internet worldwide, along with 828 UniFi Protect hosts. Around 3200 of those UniFi OS hosts were in Australia – roughly 3.1 per cent of the global total.

That’s not a small number for a market our size. Given how many UniFi consoles run cameras and doors alongside the network, you’d have to assume a fair portion of those 3200 boxes are doing security work.

At disclosure, no in-the-wild exploitation of the SAB-067 flaws had been confirmed. Having said this, recent history isn’t encouraging. The flaws in Ubiquiti’s earlier SAB-064 bulletin went from patch to botnet exploitation in around 33 days. And in June, CISA ordered the patching of 3 earlier UniFi OS flaws that attackers were exploiting to deliver a Mirai botnet loader.

We’re now well past 33 days since SAB-067 dropped. If there are UniFi consoles on your customer list that nobody has touched since August, that’s a problem worth solving this week.
The convergence problem
Why one exposed console is four exposed systems
INTERNETUNTRUSTEDUniFi OSEXPOSED TO WANNetworkSWITCHINGProtectVIDEOAccessDOORSTalkVOIPone console · one exposure · four systemsINTERNETNO FORWARDSVPNREMOTE MGMTUniFi OSPATCHED · PRIVATENetworkSWITCHINGProtectVIDEOAccessDOORSTalkVOIPforwards pulled · console reached via vpn or remote mgmt
Why it matters: Protect cameras, Access doors and Talk phones run on the same console as the network — and Censys found 100,000+ of these management interfaces on the open internet. One unauthenticated flaw reaches all four systems at once. A management interface has no business on the open internet. Pull the port forwards and reach the console via Ubiquiti’s remote management or a VPN — the SAB-067 flaws stop being remotely reachable at all.
Ubiquiti Patches 3 Maximum Severity UniFi Flaws
Ubiquiti Patches 3 Maximum Severity UniFi Flaws [ Ubiquiti Patches 3 Maximum Severity UniFi Flaws ]

What Should Installers Do?

The first job is simple: check every UniFi console you’re responsible for against the fixed versions above and update anything that’s behind. Don’t assume auto-update has done the job – log in and look.

The second job is the one that actually reduces risk. A UniFi OS management interface has no business sitting on the open internet. We’d pull port forwards and use Ubiquiti’s own remote management or a VPN instead. If a console has been exposed for weeks without patches, it’s also worth a squiz through its admin accounts and logs for anything you don’t recognise.

There’s a hardening option on the network side as well. UniFi Network 10.6, released on August 25, introduces PoE port locking. It’s the first phase of port security for UniFi PoE device connections, it’s coming to Early Access, and it needs switch firmware 7.6 or later. For camera installs, the appeal is obvious – it makes it harder for someone to unplug a camera and drop their own device onto that port.

What installers should do
Four jobs, in this order
0 of 4 worked through
The sequence is SEN’s reading of the advice in this article. Versions and the PoE port locking details (Early Access, firmware 7.6+) as stated by Ubiquiti. Tick-state isn’t saved — it’s a worksheet, not a record.

SEN’s View

In fairness to Ubiquiti, every vendor ships vulnerabilities. What counts is how quickly fixes and details reach the people who need them, and Ubiquiti published both together.

In our opinion, the bigger issue is the management model on smaller jobs. A console goes in, the cameras get tuned, the customer is happy – and nobody owns the patching after that. When a single box runs the network, the video and the doors, that gap stops being a minor IT matter and becomes a security matter.

October is Cyber Security Awareness Month, and that makes it a good moment for installers to put UniFi patching into maintenance agreements in writing. Customers will thank you for it, even if they never notice.

You can read Ubiquiti’s Security Advisory Bulletin 067 here, see Censys’ exposure analysis here or read more SEN news here.

Patch this week — then put patching in writingWe’re well past the 33 days SAB-064 took to reach botnet exploitation. Check the bulletin against every console on your list, and — with October being Cyber Security Awareness Month — put UniFi patching into maintenance agreements so the gap never reopens.Read SAB-067Censys exposure analysisMore SEN news

Features

FeaturesUniFi SAB-067 at a glance
0122 critical vulnerabilities across the UniFi range
023 rated CVSS 10.0: Protect, UniFi OS Server and Talk
03UniFi Access fixed in version 4.3.5
04Around 3200 exposed Australian UniFi OS hosts (Censys, August 27)
FixUpdate consoles and remove management interfaces from the internet.

FAQ

Quick answers · SAB-067
UniFi SAB-067 — what installers are asking
Answers restate Ubiquiti’s bulletin and Censys’ 27 August scan as reported above; two items flag what the release doesn’t state.
What is Ubiquiti Security Advisory Bulletin 067 (SAB-067)?
SAB-067, released on 26 August, fixes 22 critical vulnerabilities across the UniFi range. Three are rated CVSS 10.0 — in UniFi Protect, UniFi OS Server and UniFi Talk — and all three can be exploited remotely without credentials or any user interaction.
Which UniFi versions fix the SAB-067 flaws?
UniFi Protect 7.2.105 or later, UniFi OS Server 5.1.37 or later, UniFi Talk 5.3.2 or later, UniFi Access 4.3.5, Protect AI Key 2.2.6 and UniFi Network 10.5.67. Don’t assume auto-update has done the job — log in and check each console.
Is UniFi Access affected by SAB-067?
Yes. UniFi Access has four vulnerabilities in the bulletin (CVE-2026-77543, CVE-2026-77546, CVE-2026-77547 and CVE-2026-77553), all fixed in Access 4.3.5.
Are the SAB-067 vulnerabilities being exploited in the wild?
No exploitation of the SAB-067 flaws had been confirmed at disclosure. Recent history is less comforting: Ubiquiti’s earlier SAB-064 flaws went from patch to botnet exploitation in around 33 days, and in June CISA ordered the patching of three earlier UniFi OS flaws that attackers were using to deliver a Mirai botnet loader.
How many UniFi consoles are exposed to the internet in Australia?
Censys scanned on 27 August, the day after disclosure, and found more than 100,000 UniFi OS management interfaces exposed worldwide, plus 828 UniFi Protect hosts. Around 3,200 of the UniFi OS hosts were in Australia — roughly 3.1 per cent of the global total.
Should a UniFi OS management interface be reachable from the internet?
No. Pull the port forwards and reach the console through Ubiquiti’s own remote management or a VPN. If a console has sat exposed for weeks without patches, also review its admin accounts and logs for anything you don’t recognise.
Which UniFi hardware models does SAB-067 apply to?confirm with vendor
Hardware applicability isn’t broken down in this release — the bulletin is organised by software product and fixed version. Check Security Advisory Bulletin 067 against your installed base and confirm anything unclear with Ubiquiti.
Does installing the SAB-067 updates cause downtime?confirm with vendor
Update behaviour and reboot requirements aren’t stated in this release — confirm with Ubiquiti before patching consoles that run critical doors or cameras.
Figures and versions as published by Ubiquiti (SAB-067) and Censys. Items marked “confirm with vendor” are gaps in the release, not SEN findings.
Ubiquiti Patches 3 Maximum Severity UniFi Flaws
Ubiquiti Patches 3 Maximum Severity UniFi Flaws [ Ubiquiti Patches 3 Maximum Severity UniFi Flaws ]
”
Join the conversation
What’s your read on this?
SEN readers are the people doing the work — installers, integrators, engineers, specifiers and end users. If you’ve got hands-on experience, a correction, or a view worth arguing, put it below.
ModeratedReal names welcomeNo sales pitches

LEAVE A REPLY

Please enter your comment!
Please enter your name here

SEN News
SEN Newshttps://sen.news
Security & Electronics Networks - Leading the Security Industry with News and Latest Events. Providing information and pre-release updates on the latest tech and bringing it all to you daily. SEN News has been in print for over 20 years and has grown strong as a worldwide resource in digital media.

Latest news

ASIS ACT SAGE Seminars Announced

ASIS ACT SAGE Seminars Announced And Cover Protective Security, Risk, Facilities And Australia's Security Environment.ASIS ACT SAGE Seminars Announced...

Gallagher Security Queensland Forum Brings Industry Together

Gallagher Security Queensland Forum Brings Industry Together Across Queensland And Papua New Guinea.Gallagher Security Queensland Forum Brings Industry Together...

Acecom Installing Avigilon, Integriti At NT Art Gallery

Acecom Installing Avigilon, Integriti At NT Art Gallery In Darwin.Acecom Installing Avigilon, Integriti At NT Art Gallery - Acecom...
- Advertisement -
ASSA ABLOY Aperio IL100 – design-driven wireless access reader. Register your interest.

Dicker DAS Signs Up For SecTech Australia And SecTech NZ 2027

Dicker DAS Signs Up For SecTech Australia And SecTech NZ 2027 And Will Tour 8 Cities Across ANZ Next...

Mitchell & Brown Communications Security & Fire Acquired

Mitchell & Brown Communications Acquired By Tyler Levens And Robbie MacDonald.Tyler Levens and Robbie MacDonald have acquired Western Australian...

CMAK Technologies Wins $A2 Million Contract

CMAK Technologies Wins $A2 Million Contract To Provide City of Melville Security Solutions.CMAK Technologies Wins $A2 Million Contract -...

Must read

Neil Jarvis Appointed Enterprise & Consultant Manager, Victoria & Tasmania

Neil Jarvis Appointed Enterprise & Consultant Manager, Victoria &...

Tecom Discovery 4G TSX16000 Communications Module

Tecom Discovery 4G TSX16000 Communications Module LTE Cat 4...

Tasmania Police Plans Statewide Biometric System Replacement

Tasmania Police Plans Statewide Biometric System Replacement With Commercial...

Qolsys IQ4 NS with PowerG

Qolsys IQ4 NS with PowerG from BGW Technologies Proving...
- Advertisement -

CMAK Technologies Wins $A2 Million Contract

CMAK Technologies Wins $A2 Million Contract To Provide City of Melville Security Solutions.CMAK Technologies Wins $A2 Million Contract -...

Dicker Data To Acquire Sektor Group For NZ$138 Million

Dicker Data To Acquire Sektor Group For NZ$138 Million Expanding The Company’s Operations.Dicker Data To Acquire Sektor Group For...

TP-Link Archer 8 Ultra Wi-Fi 8

TP-Link Archer 8 Ultra Wi-Fi 8 Offers Higher Performance Over Longer Ranges In Challenging Environments.TP-Link Archer 8 Ultra Wi-Fi...

Ecos Systems Joins SecTech NZ

Ecos Systems Joins SecTech NZ And Will Bring Its Latest Solutions To 3 Cities June 2027!Ecos Systems Joins SecTech...

DroneShield Wins Potential $A716m Counter-Drone Contract

DroneShield Wins Potential $A716m Counter-Drone Contract With US Department Of Defense Joint Interagency Task Force 401.DroneShield Wins Potential $A716m...

NZ Security Installer For Sale

NZ Security Installer For Sale With 900 Residential And Commercial Customers.NZ Security Installer For Sale - A security solutions...
- Advertisement -
The people who specify, install and sign off security read SEN.Display, newsletter and sponsored content across Australia’s security industry.19,000+Monthly readers37,000+Page views200,000+Ad impressionsSee rates & specs →Google Analytics 4 · July 2026

You might also likeRELATED
Recommended to you